Tag: SecuritySifu
-
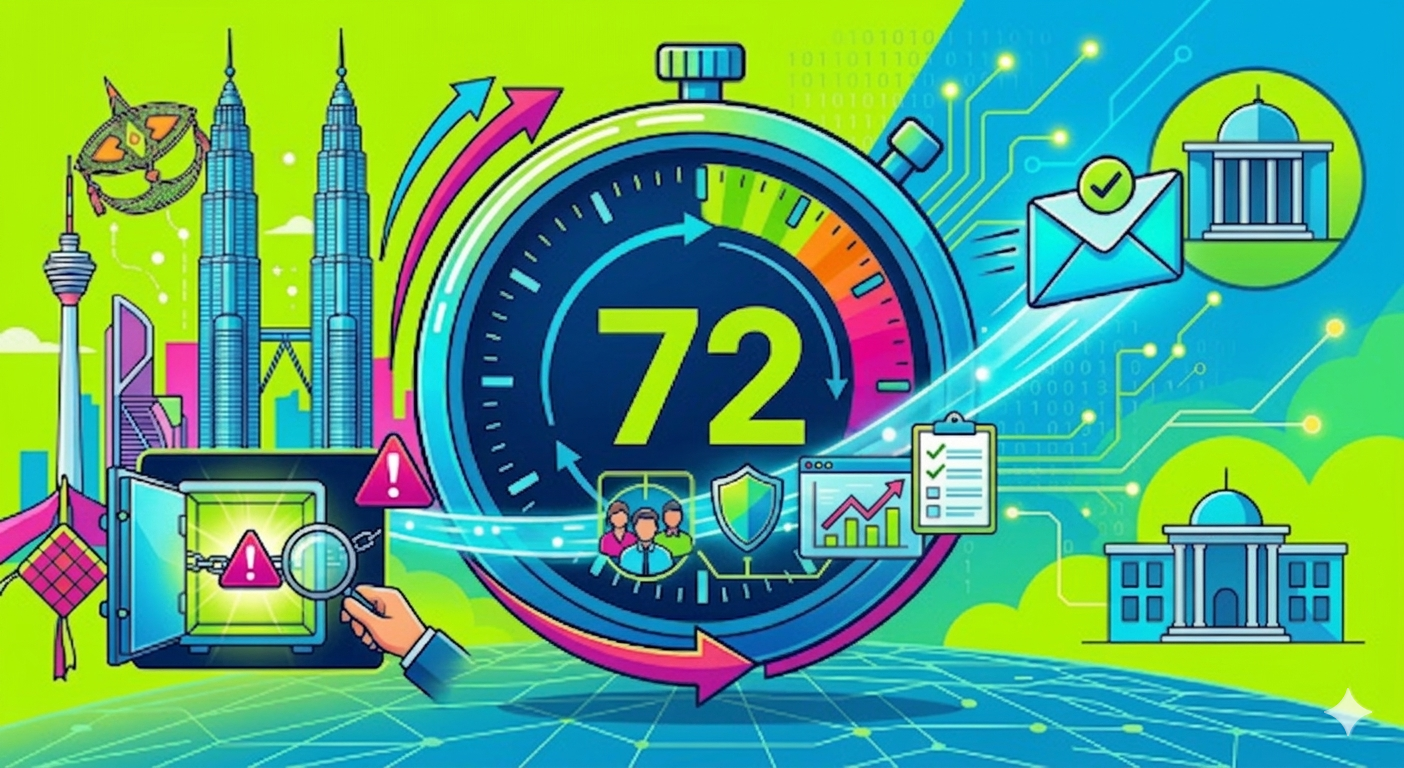
It’s 3:00 AM on a Saturday. Your Head of IT calls. There’s been an unauthorized entry into your customer database. In the past, you might have spent the next two weeks quietly investigating, patching the hole, and deciding whether to tell anyone. In 2026, the luxury of time is gone. Under the fully enforced Personal…
-
Most cybersecurity programs don’t fail during execution. They fail much earlier—at the moment they are defined, funded, and structured. By the time tools are deployed, teams are hired, and policies are written, the trajectory of success or failure is often already decided. The issue is rarely technical capability. It is almost always a lack of…
-
There’s a pattern that shows up again and again in growing companies. Revenue is climbing. Teams are expanding. New systems are being rolled out quickly. Investors are happy. And cybersecurity? It’s either: By the time leadership realizes it’s not enough, the company is already exposed. This isn’t just a technical gap—it’s a strategic timing failure.…